Which governance gaps did the Bureau of Port Security (BoPS) address, even when Indian ports already had ISPS-based assessments, approved security plans and established agency responsibilities?
Since 2004, the International Ship and Port Facility Security Code has provided the foundation for security at ports serving international shipping. Indian port facilities already assess security risks, maintain approved security plans, designate responsible officers, control access, conduct drills and adjust protective measures according to the applicable security level.
If the security framework already existed, why was the Bureau of Port Security needed? The answer is hidden in the difference between establishing security requirements and assuring their consistent implementation across a national port ecosystem. ISPS remains the international, risk-based foundation. BoPS addresses the regulation, oversight, coordination and national assurance surrounding that foundation.
"The shift is not from ISPS to BoPS, but from facility-level implementation within a distributed environment towards implementation supported by dedicated national oversight."
1. The security framework was already in place — so what was missing?
The ISPS Code entered into force through SOLAS Chapter XI-2 on 1 July 2004. It establishes an international framework through which governments, agencies, port authorities and the maritime industry assess and address threats to ships and port facilities involved in international trade. Part A contains mandatory requirements, while Part B provides guidance on implementation. The International Maritime Organization explains the ISPS framework, while DGMA describes its application in India.
At the port-facility level, two instruments remain central:
- Port Facility Security Assessment (PFSA): identifies relevant assets, threats, vulnerabilities and security needs.
- Port Facility Security Plan (PFSP): translates the assessment into approved responsibilities, procedures and protective measures.
Port Facility Security Officers, port authorities, recognised security organisations and government agencies already operated within this environment. BoPS was therefore not created because India lacked a security framework. The strategic challenge was consistency across facilities, authorities, jurisdictions and risk profiles. National assurance requires visibility into whether approved controls are applied effectively, coordinated across organisational boundaries and improved when weaknesses are identified.
2. BoPS changes the level of governance, not the foundation of security
Section 13 of the Merchant Shipping Act, 2025 authorises the Central Government to constitute a body for the security of vessels and port facilities and assigns it regulatory and oversight responsibilities. These include providing a regulatory framework, ensuring timely exchange of security-related information and coordinating with other agencies. The Act also requires the Government to consider the ISPS Code when framing the detailed rules — connecting the new institution to ISPS rather than positioning it as a replacement.
DGMA describes BoPS as a statutory body constituted under Section 13 and functioning under the Ministry of Ports, Shipping and Waterways. DGMA’s Port Security and ISPS page sets out this institutional position.
The relationship becomes clearer when the architecture is separated into three levels:
| Level | Primary purpose | Practical expression |
|---|---|---|
| ISPS framework | Defines the international security architecture and responsibilities. | Assessments, plans, security levels and assigned roles. |
| Port-facility implementation | Converts approved requirements into everyday operations. | Access control, surveillance, screening, patrols, drills and incident response. |
| BoPS oversight | Strengthens national regulation, coordination and assurance. | Standards, information exchange, inspections, reviews and inter-agency coordination. |
BoPS does not remove the need for a facility-specific assessment or plan. Nor does it convert every port into an identical operating environment. It creates a stronger institutional mechanism for examining how the existing framework is interpreted, implemented and verified across the system.
3. Why distributed responsibility creates an assurance challenge
Port security is necessarily multi-agency. Port authorities and Port Facility Security Officers manage approved facility arrangements; CISF may provide security and specialist support where deployed; and the Coast Guard, Navy, Customs, State Marine Police, intelligence bodies and other authorities operate within their respective mandates. Multiple organisations are necessary because the environment spans different jurisdictions, capabilities and risks. The assurance challenge appears at the points between them:
- Information: Who receives, validates and communicates relevant threat information?
- Authority: Does the information reach the correct facility and authorised decision-maker?
- Escalation: Are responsibilities understood across organisational boundaries?
- Verification: Can an inspection establish whether an approved control works during normal operations?
- Improvement: Are lessons from incidents and exercises converted into measurable corrective action?
Without a dedicated coordinating structure, these questions may be addressed differently across facilities and agencies. BoPS is intended to create a clearer national focal point for regulatory oversight, inspection, information exchange and coordination.
National assurance does not mean that BoPS performs every operational task. It means that distributed responsibilities can be examined as parts of one security architecture rather than as isolated institutional activities.
4. BoPS has been constituted, but the detailed rulebook is still developing
The Merchant Shipping Act, 2025, provides the statutory basis for the security body. DGMA describes BoPS as constituted, and an official July 2026 order records the assumption of charge by the Director General of Maritime Administration as Director General, BoPS.
However, the Ministry of Ports, Shipping and Waterways continues to list the Bureau of Port Security Rules, 2026 as draft. The draft states that the rules would come into force on publication in the Official Gazette. MoPSW’s draft-rules page remains the authoritative status reference as of September 2026.
| Layer | Current significance |
|---|---|
| Merchant Shipping Act, 2025 | Provides the statutory basis and high-level functions of the security body. |
| BoPS institution | Constituted as the dedicated regulatory and oversight body. |
| Detailed BoPS Rules, 2026 | Still presented by MoPSW as a draft and should not be described as final notified requirements. |
This distinction prevents both underreaction — assuming BoPS changes nothing because ISPS already existed — and overstatement, which presents proposed standards or procedures as current legal obligations. The institutional change is real, but enacted law, administrative arrangements and draft provisions must remain clearly separated.
5. What the draft rules reveal about the intended direction
Although draft provisions are not final requirements, they indicate the direction in which the oversight architecture is being developed. The draft assigns BoPS proposed functions relating to:
Regulation & Oversight
Security of vessels and port facilities.
Information
Collection, analysis and dissemination of security information.
Coordination
Liaison among Central and State Governments, ports and maritime law-enforcement agencies.
Risk & Standards
Risk-based categorisation, standards and guidance for port-facility security.
Assurance
Review of security plans, inspections, audits, reporting and corrective action.
Preparedness
Training, exercises, manuals and standard operating procedures.
These are proposed operating mechanisms, not final obligations. They nevertheless indicate a governance model in which port security becomes more consistently risk-based, reviewable and evidence-led.
"Can the port demonstrate why a control exists, how it supports the approved plan, whether it works in practice and how deficiencies are corrected? That is a more meaningful test than confirming that equipment has merely been installed."
6. The real test begins where the security plan meets operations
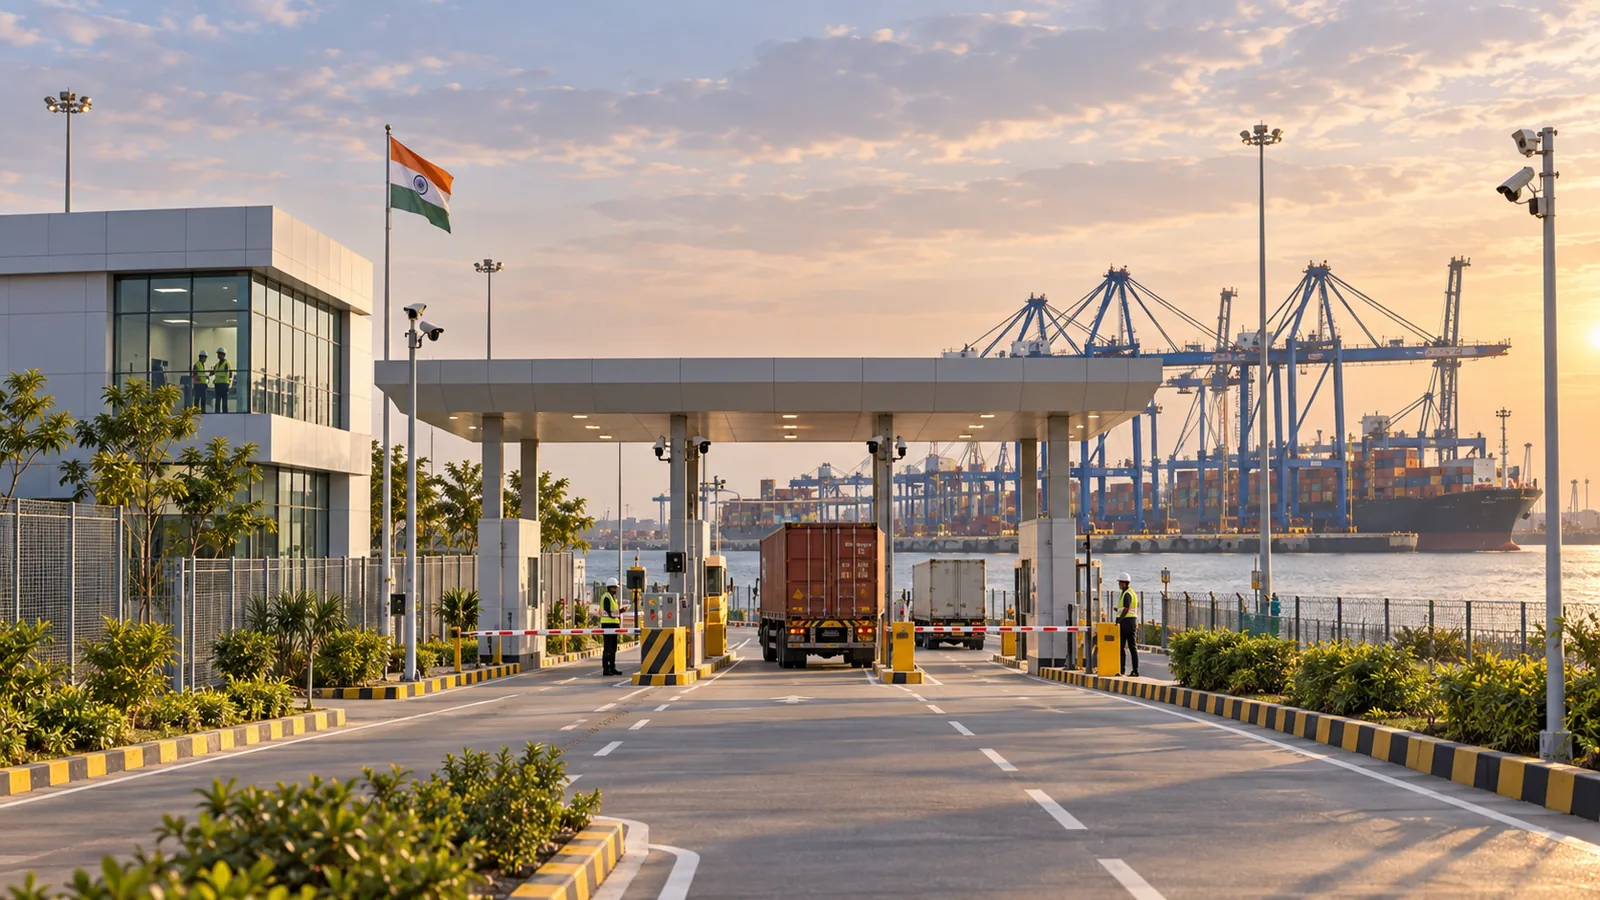
Consider an authorised contractor arriving at a restricted port area with a vehicle. Several separate controls may be involved. The sequence below is an illustrative operating scenario, not a workflow prescribed by BoPS.
If every stage functions separately, the port may still possess the required technologies and procedures. But when an exception occurs, an authorised reviewer should be able to determine:
- who requested and approved the visit;
- whether the person and vehicle matched the approved permission;
- which area and time window were authorised;
- what checks were completed at entry;
- whether surveillance or perimeter systems generated an exception;
- who received the alert and what action followed; and
- what evidence remains available for review.
The governance significance of BoPS becomes visible here: national oversight ultimately depends on the quality of everyday operational evidence.
Harbour Entry Permit, access control, ANPR, CCTV, perimeter, screening and command systems may support different parts of the approved security arrangement. Their value lies not in how many systems are installed, but in whether authorised personnel can connect information around an event, reconstruct the sequence and verify that the appropriate action was taken in accordance with the approved procedure.
7. What BoPS does not automatically change
BoPS should not be interpreted as requiring every port to rebuild its security architecture immediately. Facilities differ in cargo profile, traffic, layout, threat environment and operating constraints. A container terminal, cruise terminal, liquid-bulk facility and smaller non-major port cannot be expected to use identical controls. The Government’s stated direction is graded and risk-based, taking account of vulnerability, location and trade potential.
The draft rules also contain a proposed savings and transitional provision under which existing security plans, procedures and measures would continue until modified or superseded under the rules. Because this remains a draft provision, its final operation cannot yet be assumed.
Existing technology is not automatically obsolete. The priority is to determine whether it can support the approved security plan, exchange relevant information, maintain traceable records and accommodate future changes without unnecessary replacement.
8. What ports can strengthen without treating the draft rules as final
Ports do not need to wait passively for every detail to be finalised. They can strengthen existing ISPS-based arrangements without presenting draft provisions as mandatory.
Separate obligations from proposalsMaintain a controlled register distinguishing the Merchant Shipping Act, notified rules and directions, approved PFSA and PFSP requirements, draft provisions and internal improvement initiatives. Trace every requirement to its operating controlFor each approved security requirement, identify the responsible person, procedure, supporting system, escalation path and evidence source. Test the complete evidence chainSelect representative scenarios involving persons, vehicles, cargo areas, restricted zones, perimeter alarms and security-level changes. Test whether the port can reconstruct the event without relying on disconnected calls, screenshots or individual memory. |
Rationalise alarms and escalationAlarm severity, ownership, duplication, acknowledgement and closure rules should direct attention towards actionable exceptions rather than raw device activity. Review integration before replacementAssess whether existing access, surveillance, vehicle-management, perimeter and command systems can exchange the information required for authorised operational decisions. Close the loop after drills and incidentsObservations should lead to assigned actions, defined deadlines, verified closure and, where necessary, updates to procedures or training. |
|
Approved requirement
Operating control
Connected evidence
Corrective action
Verified improvement
|
|
Conclusion: BoPS moves the question from existence to operational efficiency
ISPS remains the foundation for security assessments, approved plans, defined responsibilities and risk-based protective measures. BoPS wraps it with a governance layer by adding a dedicated statutory focus for regulation, oversight, information exchange and coordination.
The detailed operating framework is still developing, and draft provisions must remain identified as draft. The next phase will not be defined only by whether a facility possesses a plan, procedure or technology. It will depend on whether controls are proportionate to assessed risk, connected across operations, understood by responsible personnel and supported by evidence that enables review and improvement.
"BoPS does not replace ISPS — it puts the framework to work. The measure of readiness shifts from whether a control exists to whether it can be verified across the complete operation."